by Marcus Webb | Oct 5, 2026 | Blockchain Interoperability
Cross-Chain Messaging Risks: What Is Cross-Chain Messaging?
Cross-Chain Messaging Risks begin with the challenge of making one blockchain recognize information that originated on another blockchain.
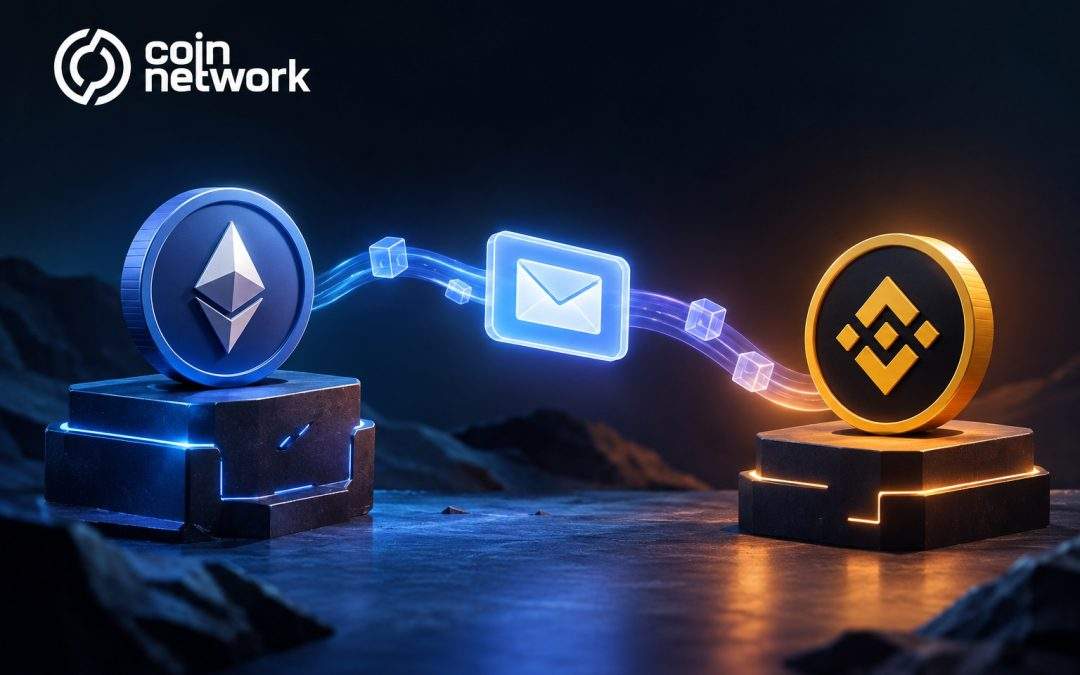
Blockchains normally operate as separate environments. Ethereum does not automatically know what happened on Solana, and a transaction on Arbitrum does not automatically become valid information on BNB Chain.
Cross-chain messaging protocols provide infrastructure that allows applications on one network to send information to another network.
That information could represent:
- A token transfer
- A governance instruction
- A contract call
- A transaction confirmation
- A price or state update
- A message requesting an action on another chain
Wormhole’s messaging documentation describes its protocol as a generic multichain messaging layer that allows applications to send arbitrary data between supported blockchain networks.
The important security question is:
How does the destination chain know that the message it received is genuine?
How Cross-Chain Messages Move Between Blockchains
Although implementations differ, a typical cross-chain message involves several stages.
1. Message Creation
A smart contract on the source blockchain emits a message or records an event.
2. Observation
A group of validators, guardians, or decentralized verifiers observes the source-chain event.
3. Verification
The verification system determines whether the event is authentic according to the protocol’s security rules.
4. Attestation
The verifiers create signatures or another cryptographic proof confirming the message.
5. Relaying
A relayer or other delivery mechanism submits the verified message to the destination chain.
6. Execution
A destination smart contract verifies the message and executes the requested action.
Wormhole’s architecture documentation describes this division between source-chain contracts, Guardian observations, signed messages, relayers, and destination contracts.
Every stage creates a separate security assumption.
A message can be cryptographically valid while the underlying source event was interpreted incorrectly. A verifier can observe the wrong state. A destination contract can contain a vulnerability. A relayer can become unavailable.
Cross-chain security is therefore a system-level problem rather than a single-signature problem.
Cross-Chain Messaging Risks and Message Verification
The most important security layer is verification.
A destination chain should not execute a valuable action merely because another blockchain claims that something happened.
It needs evidence.
Different protocols use different verification models.
Guardian Networks
Wormhole uses a Guardian Network that observes supported chains and creates signed Verifiable Action Approvals, or VAAs.
Wormhole’s current documentation states that its canonical Guardian set contains 19 Guardians, with a 13-of-19 signature threshold for a standard VAA. Wormhole’s Guardian documentation explains the current architecture.
Decentralized Verifier Networks
LayerZero uses configurable Decentralized Verifier Networks, or DVNs, to verify cross-chain messages.
LayerZero’s 2026 enterprise DVN documentation explains that applications can choose which DVNs verify their messages.
Oracle and Risk-Management Systems
Some interoperability systems combine message verification with additional monitoring, rate limits, or risk controls.
There is no universal security model.
The number of validators or verifiers matters, but so do their independence, software security, configuration, governance, and ability to detect conflicting information.
Cross-Chain Messaging Risks From Verifier Concentration
A major risk occurs when an application depends on too few independent verifiers.
If one verifier is sufficient to approve a high-value message, that verifier becomes a potential single point of failure.
The April 2026 KelpDAO incident demonstrated this risk.
Attackers stole approximately 116,500 rsETH, worth about $292 million at the time, from a LayerZero-powered bridge. Chainalysis reported that the attack compromised off-chain RPC infrastructure used by the sole DVN configured for the application and caused the system to accept a forged cross-chain message. Chainalysis’ investigation of the KelpDAO exploit explains the attack.
LayerZero’s incident report states that the application used a 1-of-1 DVN configuration, meaning one verifier’s attestation was sufficient. The report also says that the exploit did not involve a vulnerability in the underlying LayerZero protocol contracts. LayerZero’s detailed incident report provides the technical explanation.
The lesson is broader than any single protocol:
A secure messaging framework can still become vulnerable when an individual application chooses a weak verification configuration.
Cross-Chain Messaging Risks and Chain Finality
A message can only be as reliable as the source-chain event it represents.
Consider a transaction that appears on Chain A.
If the transaction has not reached sufficient finality and Chain A later reorganizes, the event may disappear or be replaced.
If a cross-chain protocol has already acted on the earlier version, the destination chain may have executed an action based on a state that no longer exists on the source chain.
Wormhole’s documentation specifically notes that when lower consistency levels are selected instead of waiting for finality, chain reorganizations can result in different VAAs appearing for what initially looks like the same message. Wormhole’s VAA documentation explains this finality issue.
This is why interoperability protocols need chain-specific finality assumptions rather than treating every blockchain as equally final.
Cross-Chain Messaging Risks and Replay Attacks
A replay attack occurs when a valid message is submitted more than once when it should only be processed once.
For example:
- Chain A produces a legitimate message.
- The message receives valid verification.
- Chain B processes it.
- An attacker attempts to submit the same message again.
- A flawed destination contract processes it a second time.
Protocols therefore use message identifiers, sequence numbers, nonces, consumed-message records, or similar mechanisms.
Wormhole’s VAAs are uniquely identified using the emitter chain, emitter address, and sequence information. The Wormhole VAA reference explains how these identifiers are used.
Replay protection is particularly important when a message can trigger token minting, withdrawals, governance actions, or other state-changing operations.
Cross-Chain Messaging Risks and Destination Contracts
Even if the source message and verification system are secure, the receiving contract can introduce risk.
A destination application might incorrectly:
- Validate message parameters
- Check token amounts
- Handle decimals
- Confirm the source contract
- Prevent duplicate messages
- Restrict authorized senders
- Apply chain-specific rules
The receiving contract must therefore verify not only that a message has a valid signature but also that it comes from the expected source application.
A legitimate message from the wrong application can still cause unintended behavior if the destination contract’s authorization logic is weak.
Cross-Chain Messaging Risks From Relayer Failures
Relayers are usually responsible for delivering verified messages to the destination chain.
A relayer may become unavailable because of:
- Network congestion
- Software problems
- Insufficient fees
- RPC failures
- Destination-chain outages
- Operational mistakes
Relayer failure is generally an availability problem rather than an integrity problem when the underlying messaging system correctly separates message delivery from message validity.
Wormhole’s security documentation, for example, states that its Executor is untrusted and can affect message-delivery timing but cannot forge or alter a valid VAA. Wormhole’s security model explains this separation.
A secure system therefore tries to ensure that a failed relayer delays a message rather than changing its contents.
Cross-Chain Messaging Risks and Governance
Governance is another important security layer.
Cross-chain protocols may have governance mechanisms capable of changing:
- Supported chains
- Validator or guardian sets
- Verification thresholds
- Contract addresses
- Rate limits
- Upgrade parameters
- Emergency controls
Those powers can be useful for responding to new threats, but they introduce additional trust assumptions.
Wormhole’s documentation states that governance actions are approved through its Guardian system, with a two-thirds supermajority required for governance actions. Wormhole’s security documentation describes the current governance model.
Researchers should therefore investigate not only technical cryptography but also who can change the rules.
Cross-Chain Messaging Risks and Chain Deprecation
A supported blockchain can also become operationally unsuitable.
Wormhole’s 2026 network update provides a useful example. The Guardian Network deprecated Scroll in April 2026 partly for security considerations and announced additional deprecations for Berachain and Injective. Wormhole’s August 2026 network update explains that network deprecation involves removing the chains from the frontend and disconnecting Guardian infrastructure.
This shows why interoperability is not purely about whether two chains can technically communicate.
Protocol operators must also continuously evaluate:
- Chain security
- Finality
- Network health
- Validator quality
- Transaction activity
- Maintenance requirements
- Long-term support
A chain becoming unsupported can affect message availability even when previously deployed contracts remain active.
Cross-Chain Messaging Risks in the 2026 Market
Cross-chain infrastructure is operating at substantial scale.
Chainlink’s metrics dashboard, updated in September 2026, reports approximately 20.17 billion total verified messages, $24.12 billion in cumulative CCIP transfer volume, and $84.16 billion in total cross-chain token value. Chainlink’s current metrics dashboard provides the underlying measurements.
These are Chainlink ecosystem metrics rather than a measurement of the entire cross-chain industry.
LayerZero reported in June 2026 that its infrastructure had moved more than $260 billion across 165 networks and carried approximately 70% of cross-chain stablecoin flow, based on its own measurements. LayerZero’s 2026 network overview provides the company’s reported figures.
Wormhole’s current materials report more than 1 billion cross-chain messages and more than $65 billion in cross-chain volume across its infrastructure, with support spanning dozens of blockchain ecosystems. Wormhole’s messaging infrastructure overview provides its current network information.
These figures should not be added together because each provider measures its own infrastructure using different methodologies.
They do, however, demonstrate the scale at which cross-chain messaging is now being used.
Cross-Chain Messaging Risks and Bridge Security
Cross-chain messaging is closely related to bridge security, but the two terms are not identical.
A bridge often uses messaging to coordinate asset movement between chains.
For example:
Lock on Chain A → verify message → mint or release on Chain B
If the message is forged, the destination bridge may release assets that are not properly backed.
Chainlink stated in April 2026 that nearly $3 billion had been stolen historically through cross-chain bridge hacks, describing insecure or centralized interoperability infrastructure as a major industry risk. This is a Chainlink estimate and should be treated as an industry estimate rather than a universal accounting of every bridge incident. Chainlink’s 2026 cross-chain security analysis provides the source and its methodology.
The KelpDAO incident further showed that cross-chain losses can originate in supporting infrastructure rather than a conventional smart-contract bug.
Cross-Chain Messaging Risks and Defense Mechanisms
Protocols can reduce risk through multiple layers of protection.
Independent Verification
Use several independent verifiers rather than relying on one entity where the application requires stronger security.
Message Replay Protection
Track unique message identifiers and prevent previously processed messages from being executed again.
Source Validation
Check the expected source chain and source contract.
Finality Rules
Wait for sufficient source-chain finality before accepting high-value messages.
Rate Limits
Limit the amount that can move across a route during a defined period.
Circuit Breakers
Pause transfers when unusual activity or inconsistent state is detected.
Cross-Chain Invariant Monitoring
Continuously compare source-chain events with destination-chain actions.
Emergency Controls
Maintain carefully governed mechanisms for stopping or containing abnormal activity.
Diverse Infrastructure
Avoid depending on a single RPC provider, verifier, relayer, or operational endpoint where feasible.
The strongest security model is generally layered rather than dependent on one mechanism.
How Users Can Evaluate Cross-Chain Messaging Risks
Before using a bridge or multichain application, check:
- Verification model: Who validates the message?
- Threshold: How many independent parties must agree?
- Source finality: How does the protocol handle reorganizations?
- Source contract: Is the expected emitting contract verified?
- Replay protection: Can a message execute more than once?
- Destination contract: How are messages authorized?
- Relayer: What happens if delivery fails?
- Rate limits: Are abnormal transfers constrained?
- Governance: Who can change security settings?
- Upgradeability: Who can upgrade the contracts?
- Monitoring: Is cross-chain state continuously checked?
- Incident history: Has the protocol experienced previous failures?
- Supported chains: Are the source and destination networks actively maintained?
For broader blockchain-security research, Coin Network’s Cryptopedia provides educational material that can be combined with individual interoperability documentation.
Common Mistakes When Evaluating Cross-Chain Messaging
Assuming a Large Validator Set Means Complete Security
The independence and actual verification process matter as much as the number of participants.
Checking Only the Bridge Contract
Off-chain RPC infrastructure, relayers, governance, and verifier configurations can also affect security.
Ignoring Source-Chain Finality
A message derived from a reorganized transaction can create inconsistent cross-chain state.
Assuming Relayers Can Forge Messages
In properly separated systems, a relayer may only control delivery timing rather than message validity. The exact architecture should be checked.
Ignoring Application-Level Configuration
The underlying interoperability protocol may support strong security while a specific application chooses a weaker verifier configuration.
Treating Audits as Guarantees
Audits can identify software issues but cannot eliminate operational, governance, configuration, or economic risks.
Cross-Chain Messaging Risks: Practical Checklist
Before transferring value or sending a cross-chain message, review:
- Message source: Which contract created it?
- Verification: Who validates it?
- Threshold: What quorum is required?
- Finality: How final is the source event?
- Replay: Is the message uniquely identified?
- Destination: Which contract executes it?
- Relayer: Who delivers it?
- Rate limit: How much value can move?
- Governance: Who can change security settings?
- Upgradeability: Who controls upgrades?
- Monitoring: Are unusual messages detected?
- Recovery: What happens after a confirmed incident?
Coin Network’s DeFi section and Ethereum coverage provide additional context for understanding interoperability, smart contracts, and cross-chain applications.
Conclusion
Cross-Chain Messaging Risks exist because one blockchain must trust information that originated somewhere else.
A secure cross-chain system therefore needs more than a bridge interface. It needs reliable source-chain observation, strong message verification, appropriate finality rules, replay protection, secure destination contracts, resilient relayers, controlled governance, and monitoring that can identify inconsistencies across networks.
The April 2026 KelpDAO incident demonstrated how a cross-chain system can be compromised through supporting infrastructure and a weak verifier configuration even when the underlying contracts are not themselves defective.
At the same time, 2026 data from Chainlink, LayerZero, and Wormhole shows that cross-chain messaging operates at significant scale, with billions of messages and tens of billions of dollars in reported transfer activity.
The key question for users and developers is therefore not simply:
“Does this bridge support my two chains?”
It is:
“How does this system prove that the message from the source chain is authentic, and what happens if one part of that security model fails?”
FAQs
1. What are Cross-Chain Messaging Risks?
Cross-Chain Messaging Risks are risks that can arise when information is transmitted and acted upon between separate blockchain networks.
They include forged messages, verifier failures, replay attacks, chain reorganizations, destination-contract vulnerabilities, relayer failures, governance risks, and configuration errors.
2. How does cross-chain messaging work?
A source contract emits a message, validators or verifiers observe it, a proof or signed attestation is produced, a relayer delivers it to another blockchain, and a destination contract verifies and executes it.
3. What is a cross-chain verifier?
A verifier is an entity, node, or network that checks whether a message from another blockchain is valid according to the protocol’s rules.
Different interoperability systems use different verifier architectures.
4. What happened in the KelpDAO cross-chain exploit?
On April 18, 2026, approximately 116,500 rsETH worth about $292 million was released from a KelpDAO LayerZero-powered bridge after attackers compromised supporting RPC infrastructure and exploited a 1-of-1 DVN configuration.
The incident demonstrated why verifier diversity and infrastructure security matter.
5. Can cross-chain messages be replayed?
They can be a risk if a destination contract does not correctly track processed messages.
Secure messaging systems generally use unique message identifiers, sequence numbers, nonces, or equivalent mechanisms to prevent duplicate execution.
6. Why is source-chain finality important?
A cross-chain system may act on an event before the source blockchain considers it sufficiently final.
If the source chain reorganizes afterward, the destination chain could have acted on a state that no longer represents the source chain’s canonical history.
7. Can a relayer forge a cross-chain message?
That depends on the protocol.
In Wormhole’s architecture, the relayer is considered untrusted and can affect delivery timing but cannot forge a valid VAA without the required Guardian signatures. Wormhole’s security documentation explains this model.
8. Is a 13-of-19 Guardian system completely trustless?
No.
A threshold-signature system still creates trust assumptions around the Guardian set, governance, infrastructure, software, and the source chains being observed.
Wormhole currently uses 19 canonical Guardians and a 13-of-19 VAA threshold.
9. What are DVNs?
DVNs, or Decentralized Verifier Networks, are verification components in LayerZero’s messaging architecture.
Applications can configure which DVNs verify their messages and how those verifiers are combined.
10. How can cross-chain bridge risks be reduced?
Important mechanisms include independent verification, finality checks, replay protection, source-contract validation, rate limits, circuit breakers, monitoring, and carefully governed emergency controls.
11. What is the scale of cross-chain messaging in 2026?
Chainlink’s September 2026 metrics report approximately 20.17 billion verified messages and $24.12 billion in cumulative CCIP transfer volume.
LayerZero reports more than $260 billion moved across 165 networks, while Wormhole reports more than 1 billion messages and over $65 billion in cross-chain volume across its infrastructure.
These figures come from individual providers and should not be combined because their methodologies differ.
12. Where can I learn more about Cross-Chain Messaging Risks?
For technical research, see Wormhole’s messaging architecture, Wormhole’s security model, LayerZero’s 2026 DVN documentation, and Chainlink’s 2026 cross-chain security analysis.
For broader crypto education, Coin Network’s Cryptopedia, DeFi resources, and Ethereum coverage provide additional background.