









Blockchain tracking specialists estimate that bad actors extracted upwards of $93 million from digital wallets configured on devices supplied by authorized reseller CryptoBilis. Ledger confirmed that an unauthorized hardware implant was identified inside at least one victimized unit, while stablecoin issuer Tether moved to freeze $10 million in USDT associated with the breach.
The thefts target the foundation of cold-storage security, attacking physical equipment engineered to insulate private credentials entirely from digital threats. Ledger reported that its direct retail pipelines and underlying network servers experienced no operational intrusions, pointing instead to equipment sourced via its partner in Southeast Asia.
Reseller CryptoBilis Halts Hardware Distribution
Ledger initiated its formal inquiry on Friday, October 9, 2026, after users in Southeast Asia reported widespread asset losses from units bought through reseller CryptoBilis. The vendor serves as an authorized distributor across Indonesia, Malaysia, and the Philippines, according to The Block. Reseller CryptoBilis has since halted all retail hardware sales while the investigation progresses.
In a 72-hour operational statement issued on Sunday, Ledger maintained that every confirmed theft connected to the October 9 episode traces exclusively to reseller CryptoBilis. The hardware manufacturer classified the volume of affected units as limited, noting that it had engaged relevant public authorities alongside emergency security consortium SEAL 911.
The manufacturer reiterated guidance instructing CryptoBilis purchasers to leave unboxed units unconfigured. For owners who have active balances on those devices, Ledger urged immediate fund migrations over to fresh equipment configured with newly generated seed phrases.
Tracking the Millions Siphoned From Wallets
Blockchain intelligence company Bitquery reported calculating $93.2 million extracted from 315 wallets across six separate blockchains between Friday, October 9, and Saturday, October 10. Ledger has not authenticated that sum or confirmed an official figure for aggregate user balances lost.
Alternative estimates illustrate the uncertainty across distributed ledgers. Onchain analyst Specter logged upwards of $86 million stolen across Ethereum, Tron, and Bitcoin, Decrypt reported. YFarmX documented transmitting an inventory exceeding 450 compromised wallets to Ledger for inspection.
Analysts note that counting individual compromised addresses does not correspond to an exact total of victims, as a single investor routinely operates multiple deposit points, nor does the timing of an initial transaction verify when equipment was bought. Tether intervened roughly ten minutes after early public disclosures, ultimately locking 37 addresses, twenty of which secured $10 million in USDT.
A substantial portion of the diverted capital shifted across specialized conversion platforms. Bitquery confirmed that 2,990 ETH was routed through coin mixer Tornado Cash and onward through Zcash, with $81 million remaining traceable across public distributed ledgers as of October 11.
Inspection of Hardware Alterations
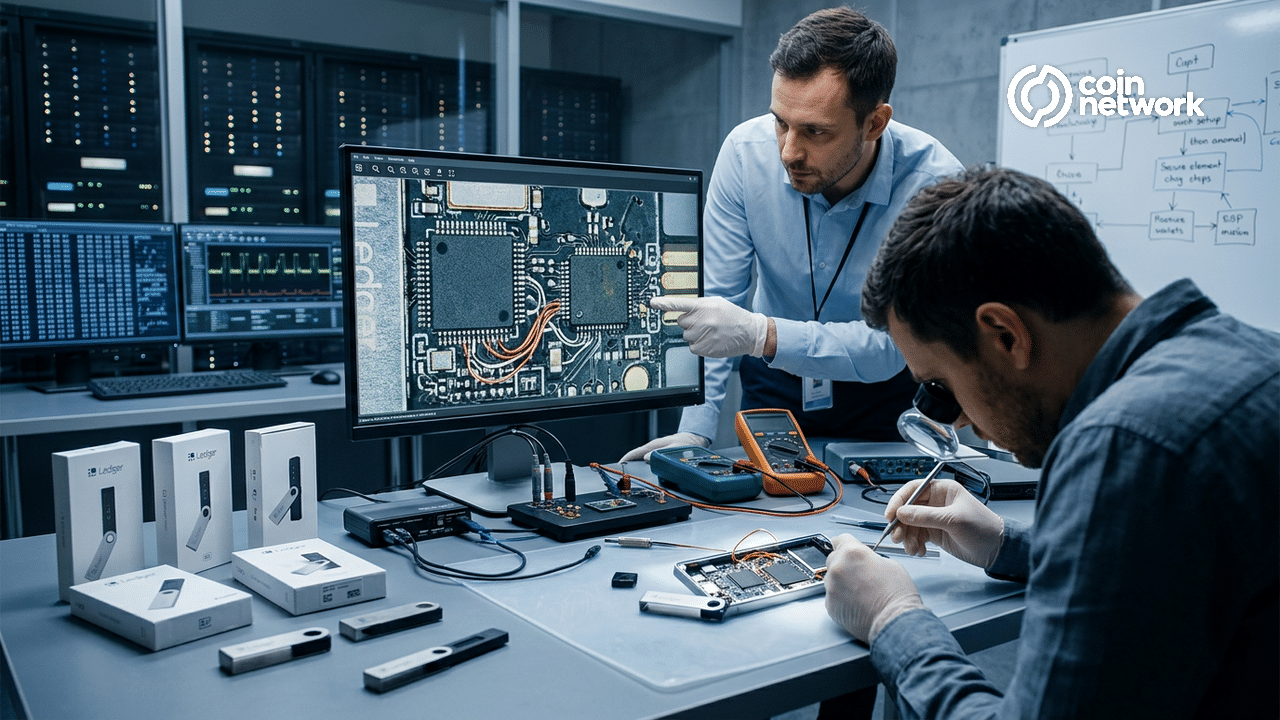
Former Mt. Gox executive Mark Karpelès shared teardown imagery on October 9 of a Ledger Nano X bought in Malaysia, displaying extra internal electronics seated behind the visual screen where standard cushioning normally rests. Karpelès has not established that the scrutinized unit originated from reseller CryptoBilis.
The illicit modification is configured to intercept the 24-word recovery phrase off the internal display bus during initial onboarding, relaying the keys externally via mobile connectivity without alerting connected computers or personal phones. Software developer 0xQuit noted that some users could alternatively have fallen victim to phishing scams, calling broad accusations of a core Ledger hack irresponsible, CryptoTicker reported.
Unverified claims of tampered devices surface beyond Southeast Asia. Social platform user Johannes reported finding units in European retail settings featuring modified internals, though Ledger maintains that all verified compromises remain isolated to CryptoBilis inventory, Decrypt reported. Decrypt submitted an inquiry to Ledger regarding the European allegations, while Karpelès's post referencing the report remains an unverified lead.
Supply Chain Vulnerabilities and Industry Repercussions
Ledger's public stance framing the issue as isolated strictly to reseller CryptoBilis prompted friction online because the vendor was promoted on the firm's official partner directory. Online commentator MyCryptoParadise argued that an authorized vendor breach cannot be separated from Ledger itself.
The crypto security landscape has navigated repeated hardware and third-party disruptions throughout the period. Ledger addressed a logic bug within its Ethereum software client in late August, and shipping vendor ShipMonk experienced a data exposure that compromised private contact details for 13,689 Trezor customers.
The current episode poses distinct challenges by circumventing the isolated environment expected from offline cold-storage hardware. Ledger highlighted that its proprietary backend infrastructure survived without intrusion, contrasting with an unrelated April software phishing incident where counterfeit Ledger Live applications extracted over $9.5 million through voluntary user disclosures.
To mitigate future hardware exposure, Ledger reiterated that authorized partner distributors must source inventory through approved routes and never restock previously returned customer merchandise. The company also urged crypto investors to procure hardware solely via direct manufacturer websites or vetted authorized distribution partners.
Conclusion
Ledger has confirmed an unauthorized hardware implant inside an affected device, while blockchain researchers trace upwards of $93 million extracted from wallets linked to products sold by reseller CryptoBilis. With Tether freezing $10 million in USDT and roughly $81 million remaining visible across public ledgers as of October 11, CryptoBilis has suspended hardware transactions during the active investigation.
Ledger continues working alongside international law enforcement and SEAL 911 to evaluate its reseller network, while reviewing distributor practices to prevent returned equipment from re-entering retail inventory.
Frequently Asked Questions
How much cryptocurrency was taken from devices sold by reseller CryptoBilis?
Blockchain intelligence company Bitquery reported that $93.2 million was drained across six blockchains, while analyst Specter tracked over $86 million in losses across Ethereum, Tron, and Bitcoin. Ledger has not officially validated these loss estimates.
What hardware modification was identified in the compromised Ledger units?
Ledger confirmed on October 10, 2026, that an affected user's device housed an unauthorized hardware implant. Teardowns revealed internal modifications capable of intercepting secret 24-word recovery phrases from the display connection during initialization and broadcasting them over cellular signals.
Which regions and vendor channels does reseller CryptoBilis serve?
CryptoBilis was featured as an authorized Ledger reseller serving Indonesia, Malaysia, and the Philippines. Following the wallet-draining events, CryptoBilis halted all sales of hardware wallets pending the outcome of the security inquiry.
What actions did Tether take regarding the stolen funds?
According to Bitquery, Tether began blacklisting addresses within minutes of initial alerts, successfully locking 37 addresses. Twenty of those addresses held approximately $10 million in USDT tied to the heist.
Sources
- Ledger Hack Drains $93 Million From CryptoBilis Wallets, Hardware Implant Found
- Ledger Says All Confirmed Cases in Suspected $87M Drain Tied to Reseller CryptoBilis
- Ledger claims CryptoBilis cases are limited as up to $93 million is traced, $10 million frozen
- Ledger Says All Confirmed Cases Trace to Reseller CryptoBilis, Gives No Loss Total