A long-inactive dormant Ethereum address holding 12,746 ETH has reactivated after sitting motionless for roughly 10.2 years, blockchain tracking service Whale Alert reported. The stash of tokens is valued at approximately $31.7 million, according to Coinfomania.
The transaction marks the first on-chain transfer from the wallet in more than a decade, according to Coinfomania and Crypto Briefing. The sudden motion has attracted attention across the cryptocurrency sector as observers track whether the assets will enter the open market.
Coinfomania noted that the activation of a dormant address carrying significant balances often commands strong attention from market participants who monitor wallet behavior. Whale Alert flagged the initial transaction after logging the sudden movement of the 12,746 ETH balance, according to Crypto Briefing.
Activation Details and Wallet History
Blockchain tracking platform Whale Alert observed the activation of the dormant Ethereum address, which held exactly 12,746 ETH prior to the movement, Crypto Briefing reported. The confirmed portion of the event remains the wallet activation itself.
The assets sat untouched for about 10.2 years before the current transaction, according to Crypto Briefing. Coinfomania reported that the 12,746 ETH stored within the wallet carried an estimated worth of $31.7 million at the time of the reactivation.
Crypto Briefing reported that public records have not established where the coins were transferred or what the wallet owner plans to do next. The early-era wallet joins an expanding roster of historically quiet cryptocurrency addresses coming back into service.
Coinfomania reported that a dormant Ethereum address valued at $31.7 million had resumed activity after more than ten years of inactivity. The outlet noted that the wallet held 12,746 ETH undisturbed before its sudden awakening.
Patterns Across Resurfacing Early Accounts
The movement is not an isolated event among legacy holders, according to Crypto Briefing. Throughout 2025 and 2026, multiple dormant accounts resurfaced on-chain, including separate transactions involving 10,000 ETH, 2,000 ETH, and 40,000 ETH.
On-chain monitoring services including Lookonchain, Arkham Intelligence, Whale Alert, and block explorer Etherscan have consistently tracked transactions from these historical wallets, Crypto Briefing reported. Many of these addresses belong to investors who took part in Ethereum's original initial coin offering.
An initial coin offering functions as a capital-raising mechanism where a project offers tokens directly to the public ahead of or around its network launch, Crypto Briefing noted. Early participant purchase costs were comparatively small, with some accounts acquiring substantial ETH balances for as little as $3,100, generating steep returns at contemporary valuations.
Crypto Briefing noted that the economics underpinning those original early purchases are striking given subsequent network growth. Those early buyers who held through multiple market cycles now command tens of millions of dollars in total value from modest baseline outlays.
Typical Behavior for a Dormant Ethereum Address
Blockchain analytics firms monitoring veteran wallets have noted consistent behavioral patterns, according to Crypto Briefing. Owners who hold a dormant Ethereum address typically initiate activity with a minimal test transaction before transferring larger sums once operational safety is verified.
Historical outcomes following the return of inactive accounts have diverged, Crypto Briefing reported. Some participants route digital assets directly to centralized exchanges, a pattern commonly seen prior to asset sales, while other investors deposit their holdings into staking arrangements.
Staking requires locking tokens to assist in validating and securing the underlying blockchain in exchange for programmatic payouts, Crypto Briefing explained. Data shows several returning accounts preferred yield generation over liquidating positions, demonstrating that certain early buyers prioritize network yield over converting tokens to cash.
Coinfomania explained that Ethereum functions as a decentralized platform supporting smart contracts and decentralized applications. As the network's health and user engagement continue to evolve, transactions originating from ancient wallets draw heightened scrutiny from market participants.
Market Scrutiny and Future Flow Analysis
The reactivation of the dormant Ethereum address holding $31.7 million in assets may bring increased scrutiny to the tactical behavior of major market participants, according to Coinfomania. The publication noted that traders are advised to observe how markets respond to the movement.
Market participants are monitoring whether subsequent transfers create spot selling pressure or signal long-term retention, Coinfomania and Crypto Briefing reported. In previous instances, individual wallet reactivations were processed by the market without triggering severe ETH price volatility, according to Crypto Briefing.
Market analysts emphasize that subsequent transfers will provide clearer direction than the initial wake-up transaction, Crypto Briefing reported. Movements directed toward exchange deposit infrastructure would suggest liquidation intent, whereas transfers to staking contracts point toward continued holding.
Coinfomania reported that trading volumes remain low and Ethereum market dynamics are currently fluctuating with mixed conditions. Market dynamics can shift rapidly during large transactions, sparking speculation regarding whether early whales plan to divest or hold.
The reactivation reported by the Whale Alert tracker could indicate strategic positioning or renewed interest within the ecosystem, Coinfomania reported. Traders remain keen to monitor whether price moves follow as market participants absorb the return of the historical wallet balance.
Conclusion
Blockchain monitoring confirmed that the dormant Ethereum address carrying 12,746 ETH stirred after roughly 10.2 years of inactivity, with the underlying stash valued at $31.7 million. Public records have not disclosed the recipient address or the asset owner's ultimate objective.
Market observers continue to watch on-chain explorers to see whether follow-up transactions transfer the assets into exchange accounts for liquidation or deposit them into network staking contracts.
Frequently Asked Questions
How much cryptocurrency did the dormant Ethereum address hold?
The address contained 12,746 ETH, which was valued at approximately $31.7 million at the time of its activation, according to Coinfomania and Crypto Briefing.
How long was the 12,746 ETH address inactive?
The wallet remained completely untouched on the blockchain for approximately 10.2 years before its first transaction was observed by tracking services, Crypto Briefing reported.
Who initially reported the movement of the 12,746 ETH?
Blockchain tracking platform Whale Alert flagged the initial movement of the 12,746 ETH after monitoring the long-silent address coming online, according to Crypto Briefing.
Where were the 12,746 ETH coins transferred?
Public reporting has not established the destination of the coins or the intention behind the transfer, leaving the wallet activation as the only confirmed detail, according to Crypto Briefing.
Ripple has resolved an XRP Ledger bug that originated in 2015, which could have enabled bad actors to generate billions of unauthorized XRP tokens without paying for them. The critical defect broke the core protocol mechanics governing the asset by circumventing the network's strict issuance limits, according to reports from CoinDesk and Crypto Briefing.
The discovery touches the fundamental architecture of the ledger, which was launched in 2012 with a hard-coded supply limit of 100 billion XRP. Software rules established at inception prevent any additional units from entering circulation, making protocol-level protection paramount for institutional participants relying on the immutable cap.
Engineers confirmed the severity of the flaw by recreating it on an isolated testing system. The demonstration showed that newly produced tokens generated through the exploit could subsequently be transferred and spent across external venues.
Mechanics Behind the XRP Ledger Bug
A security review published on Friday detailed how the vulnerability stemmed from an internal arithmetic flaw within the decentralized trading system embedded directly into the payment network. CoinDesk reported that the counting discrepancy would have let an attacker acquire vast quantities of tokens while paying virtually nothing in return.
The conceptual assault required an operator to establish several hundred separate profiles across the XRP Ledger. Each controlled address would submit an order proposing to trade an insignificant slice of an alternative asset in exchange for an excessively large balance of XRP.
Executing the attack involved dispatching one unified transaction designed to purchase every open proposal concurrently. Because the cumulative balance of XRP reached levels beyond what the software could properly track, the arithmetic overflow malfunctioned. As a result, the seller accounts received their payouts in full, while the buyer account surrendered almost no capital, effectively minting freshly created tokens out of thin air.
Evading Ledger Balance Checks
The XRP Ledger contains automated verification routines engineered to audit token balances and ensure no unapproved supply enters the ecosystem after a transaction settles. However, CoinDesk reported that because this validation mechanism depended on the miscalculated sum produced by the software flaw, the routine failed to recognize that unbacked units had appeared.
The design of the exploit also bypassed built-in transfer thresholds. Safeguards restricting the volume of tokens a single destination wallet can receive were avoided entirely by dispersing the generated funds across hundreds of smaller receiving addresses.
Carrying out this exploit method required minimal initial capital from an attacker. Security researchers determined that an operator needed only a few hundred XRP to configure the target wallets, with the vast majority of that reserve fully recoverable alongside base transaction charges.
Discovery and Protocol Safeguards
The XRP Ledger bug was discovered by security researcher Cayden Liao working alongside Veria AI, who communicated their findings to network maintainers in September. Following that notification, RippleX programmers replicated the attack vector internally to assess the danger.
Addressing the XRP Ledger bug allowed developers to ensure that the network's hard cap remained completely intact without requiring structural shifts. Crypto Briefing reported that the remediation maintained existing operational parameters without changing circulating balances or the predetermined release schedule managing Ripple's escrow reserves.
Eliminating the XRP Ledger bug helped reinforce market confidence in the underlying software framework as XRP contends with industry competition and ongoing legal requirements across various jurisdictions.
Market Reaction and Price Trajectory
Market participants have viewed the resolution of the XRP Ledger bug as a positive signal for future structural reliability, which could play a role in shaping asset valuations over time. Analysts suggest the repair helps remove uncertainty surrounding the network's foundational security.
Despite the long-term stabilization implied by resolving the XRP Ledger bug, short-term speculative sentiment saw little movement. The prediction market pricing the likelihood of XRP reaching an all-time high by the close of 2026 stood at a 5.8 percent probability, reflecting muted immediate reaction to the security news.
Market analysts pointed out that broader macroeconomic pressures continue to exert a strong influence on digital assets. Shifts in Bitcoin valuation and changes in monetary policy from the U.S. Federal Reserve remain pivotal factors that could guide the market direction of XRP alongside protocol developments.
According to Crypto Briefing, market observers note that monitoring upcoming statements from Ripple leadership or associated regulatory shifts will remain crucial for evaluating market confidence. Technological updates and token adoption milestones will also be watched closely to gauge whether XRP can hit new highs by late 2026.
Conclusion
The resolution of the dormant 2015 software flaw protects the fixed 100 billion token supply of the XRP Ledger by eliminating a method that could have allowed counterfeit tokens to reach secondary exchanges. Moving forward, observers are tracking upcoming executive commentary from Ripple, regulatory updates, and ecosystem milestones regarding institutional adoption and technology rollouts that could shape the likelihood of the token reaching record price levels by the end of 2026.
Frequently Asked Questions
What was the XRP Ledger bug discovered in the software?
The issue was a dormant calculation error dating back to 2015 located within the ledger's built-in exchange. It would have enabled an attacker submitting simultaneous offers across hundreds of accounts to cause a counting failure, generating unbacked XRP while charging the buyer almost nothing.
Who identified the vulnerability in the XRP Ledger?
Researcher Cayden Liao and Veria AI identified the vulnerability and reported the problem internally to developers in September, according to CoinDesk.
Did the vulnerability alter the 100 billion XRP token supply?
No. The fix preserved the existing ledger mechanics without altering current balances or the hard cap of 100 billion tokens set at the network's 2012 launch.
How did prediction markets react to news of the software fix?
The probability of XRP touching a new all-time high by the end of 2026 remained unchanged at 5.8 percent on prediction markets, demonstrating limited immediate price response, according to Crypto Briefing.
The RBI cautious on crypto stance was reaffirmed on Saturday, with Governor Sanjay Malhotra saying India continues to treat digital assets warily while actively supporting the technologies that underpin them. Speaking at the fifth Kautilya Economic Conclave in New Delhi, Malhotra said the central bank backs innovation in distributed ledger technology and tokenisation but remains guarded about crypto assets themselves.
The remarks matter because they reaffirm the RBI's long-held position at a time when India is developing its own digital rupee and applying tax and compliance rules to private digital assets. Malhotra's comments draw a clear line between the technology, which the central bank is already exploring, and private cryptocurrencies, which it views as a risk to monetary stability.
Why the RBI Cautious on Crypto Position Persists
Malhotra said India's concerns about cryptocurrencies centre on monetary sovereignty, the conduct of monetary policy and the management of capital flows. He linked the issue to the concept of the singleness of money, the idea that money should hold a uniform value, and warned that alternative forms of money could weaken monetary policy transmission.
The risks are especially acute for emerging market economies that maintain restrictions on capital flows, he said. ANI reported that the governor flagged worries over the singleness of money and the conduct of monetary policy, and he pointed to the complications that arise where capital movement is controlled.
The governor separated the tools behind digital assets from the assets themselves, Outlook Money reported. He said the central bank endorses these tools and has already put some of them into use, with certain applications being explored by the RBI and through public-private partnership initiatives.
Cross-Border Payments and the Digital Rupee
The governor argued that the problem crypto assets claim to solve is not domestic payments, which in India and many other countries are already efficient. "The problem that you are trying to address is primarily not so much of domestic payments, because domestic payments within our country and in many countries now are quite fast, cheap and convenient," he said.
The more significant challenge, Malhotra said, lies in cross-border payments, where he suggested central bank digital currencies could offer a solution. He said other options, including CBDCs, can be explored to improve international transactions, placing the digital rupee within the debate on upgrading cross-border payment systems without relying on private cryptocurrencies.
The RBI has been building and trialling the digital rupee even as it holds a guarded line on private crypto assets. The RBI cautious on crypto approach pairs support for financial technology with strict oversight of private digital assets, which remain outside the country's official currency system even as they are subject to tax and compliance requirements.
Bond Yields, Debt and Monetary Policy
Turning to global economic conditions, Malhotra addressed rising public debt and hardening bond yields worldwide. He said yield movements are essentially a function of demand and supply, with spending by governments and private enterprises increasing, including expenditure driven by artificial intelligence.
Malhotra said, "Money is scarce, spending has increased, both by the government as well as private enterprises, led by AI, and so that's what is leading to the hardening of the bond yields and debts."
On monetary policy, Malhotra said the RBI's approach remains primarily focused on domestic growth and inflation dynamics. He added, however, that global interest rates also have implications for India, including through their effect on real interest rates in the country. "That is something that we need to take care of," he said, noting that the central bank must remain attentive to international rate movements.
Financial Stability and the Limits of Resilience
Malhotra delivered a special address titled "Preserving Financial Stability in an Evolving World" at the conclave on 3 October 2026, according to PSU Connect. He cautioned that the financial system's current resilience should not be mistaken for protection against future vulnerabilities and called for continued vigilance.
Malhotra said, "Today's resilience may not necessarily imply tomorrow's immunity, and we are committed to remain vigilant of emerging vulnerabilities and continue to keep our financial system strong and resilient," pointing to the healthy balance sheets of banks and non-banking financial companies. He recalled that cleaning up the bad-loan legacy left by the excessive lending of the early 2000s took close to ten years, and invoked Minsky's Financial Instability Hypothesis to warn that prolonged stability can encourage excessive risk-taking.
He said shocks, whether originating inside or outside the system, cannot be avoided, so the goal should be a financial system that keeps delivering services even under severe stress. Malhotra concluded with five priorities for policymakers, including accepting that some shocks are inevitable, strengthening data and monitoring, ensuring resilience across the entire financial system and making sure innovation reinforces rather than erodes trust, PSU Connect reported.
Conclusion
Malhotra's remarks at the Kautilya Economic Conclave reaffirm the RBI cautious on crypto framework: wariness of private cryptocurrencies over concerns about monetary sovereignty, policy and capital flows, alongside active support for distributed ledger technology, tokenisation and the digital rupee. The central bank continues to develop and test its CBDC while private crypto assets remain outside India's official currency system. The next concrete step in this framework is the RBI's ongoing work on the digital rupee as a potential tool for cross-border payments.
Frequently Asked Questions
What did RBI Governor Sanjay Malhotra say about cryptocurrencies at the Kautilya Economic Conclave?
Speaking at the fifth Kautilya Economic Conclave in New Delhi on Saturday, Malhotra said India continues to treat cryptocurrencies with caution, citing worries over monetary sovereignty, the conduct of monetary policy and capital flows, while supporting innovation in the underlying technologies such as distributed ledger and tokenisation.
Why is the RBI cautious about crypto assets?
Malhotra said cryptocurrencies raise concerns related to the singleness of money and their potential impact on monetary policy. He added that the risks are greatest for emerging market economies that maintain controls on capital flows, and he linked the debate to monetary sovereignty.
What did Malhotra say about CBDCs and cross-border payments?
The governor said the more significant challenge is cross-border payments, not domestic payments, which are already fast, cheap and convenient in India. He said other solutions, including central bank digital currencies, can be explored to improve international transactions.
What did the RBI Governor say about rising bond yields and global debt?
Malhotra said yield movements are driven mainly by demand and supply conditions, as spending by governments and private companies climbs, including outlays tied to artificial intelligence. He said money is scarce and spending has increased, which is leading to the hardening of bond yields and debts.
How is India regulating private cryptocurrencies while developing the digital rupee?
The central bank is building and trialling its digital rupee even as it keeps a guarded stance toward private crypto assets. Transactions in such assets fall under tax and compliance rules, yet private cryptocurrencies still sit outside the country's official currency framework.
Crypto Oracle Manipulation occurs when attackers influence, exploit, or deceive the price-data mechanism used by a blockchain application.
Smart contracts cannot directly access external market information. A DeFi lending protocol, derivatives platform, or synthetic-asset system therefore needs an oracle to provide prices such as ETH/USD, BTC/USD, or the value of a collateral token.
If the protocol receives an incorrect price, it can make incorrect financial decisions.
For example, an inflated collateral price could allow an attacker to borrow more assets than the collateral is genuinely worth. An artificially low price could trigger unnecessary liquidations.
Chainlink’s explanation of data quality for DeFi describes why single-market dependencies, poor market coverage, outliers, and rapid volume shifts can create vulnerabilities in oracle designs.
The key question is:
Can an attacker influence the price that the smart contract ultimately trusts?
How Crypto Price Oracles Work
A price oracle acts as a bridge between blockchain applications and external or market-derived information.
There are several different designs.
Exchange-Based Oracles
These use prices from one or more exchanges.
Decentralized Oracle Networks
Multiple independent nodes collect and report data, which is then aggregated.
On-Chain DEX Oracles
These derive prices from decentralized-exchange liquidity pools or other blockchain data.
Time-Weighted Oracles
A TWAP uses prices observed over a period rather than relying on a single instantaneous price.
Each approach has different strengths and weaknesses.
A strong oracle design generally considers source diversity, liquidity, market coverage, update frequency, outlier handling, and failure conditions.
Why Crypto Oracle Manipulation Can Cause DeFi Losses
The impact comes from how deeply price feeds are connected to DeFi protocols.
A lending platform may use an oracle to determine:
Collateral value
Loan-to-value ratios
Liquidation thresholds
Borrowing power
Liquidation prices
A derivatives platform may use an oracle to determine:
Mark prices
Funding calculations
Liquidation conditions
Settlement values
A synthetic-asset protocol may use an oracle to determine:
Minting ratios
Redemption values
Collateral requirements
If the price input becomes unreliable, the application can execute rules based on an incorrect valuation.
That does not necessarily mean the oracle itself was hacked. The underlying weakness may be a thin market, poor aggregation, stale data, insufficient validation, or incorrect protocol assumptions.
Crypto Oracle Manipulation Through Thin Liquidity
One common attack involves manipulating the market that an oracle observes.
Suppose a protocol obtains the price of a token from a small DEX pool.
If the pool has only limited liquidity, a large trade can move its price dramatically.
An attacker may:
Borrow capital, potentially through a flash loan.
Trade heavily against the thin pool.
Push the observed token price upward or downward.
Cause the oracle to report the distorted value.
Use the incorrect price inside a lending or trading protocol.
Extract assets at the manipulated valuation.
Reverse the market position and repay the temporary liquidity.
The attacker does not necessarily need to control the oracle software directly.
They can instead manipulate the data source the oracle trusts.
Chainalysis describes this mechanism in its analysis of oracle manipulation attacks, noting that attackers can use large amounts of capital to rapidly increase activity in low-liquidity markets and create prices that do not represent the wider market.Chainalysis’ oracle manipulation analysis provides additional technical context.
Crypto Oracle Manipulation and Flash Loans
Flash loans can make some attacks more capital-efficient.
A flash loan allows a user to borrow assets and repay the loan within the same blockchain transaction, provided the transaction satisfies the lending protocol’s conditions.
An attacker can therefore access a large temporary pool of capital without maintaining the same amount of capital beforehand.
That does not make every flash-loan transaction malicious. Flash loans also have legitimate DeFi uses such as arbitrage and refinancing.
The security issue occurs when temporary liquidity is used to manipulate a price source that a protocol treats as trustworthy.
The January 2026 Makina exploit provides a recent example. Attackers used a 280 million USDC flash loan, with approximately 170 million USDC used to distort Makina’s MachineShareOracle before roughly 110 million USDC was traded against a DUSD/USDC Curve pool holding only around $5 million in liquidity. The reported loss was approximately $4.13 million.CoinDesk’s report on the Makina exploit describes the attack and the affected pool.
The example shows why the liquidity and methodology behind an oracle matter as much as the oracle contract itself.
Crypto Oracle Manipulation and Stale Prices
Not every bad price is caused by active manipulation.
A price feed can also become stale.
A stale price occurs when the reported value is no longer sufficiently aligned with current market conditions.
This can happen because of:
Network congestion
Oracle node problems
Data-provider outages
Insufficient update frequency
Market inactivity
Broken integration logic
A stale oracle can become dangerous during sharp market movements.
For example, suppose ETH falls rapidly from $3,000 to $2,500 while a protocol continues using an older $3,000 price.
Borrowers could temporarily appear better collateralized than they really are.
Similarly, a stale price can delay appropriate liquidations and increase losses if the market continues moving.
Crypto Oracle Manipulation Through Single-Source Data
A single-source oracle has an obvious weakness: one source can become a single point of failure.
If a protocol uses only one exchange’s price, an attacker may target that market.
Even if the exchange itself is legitimate, its price may temporarily diverge from the broader market because of:
Thin liquidity
A large isolated trade
Exchange outages
Regional market differences
Market-maker withdrawal
Abnormal volatility
Chainlink’s data-quality research explains why relying on a single exchange can produce inaccurate prices when market share shifts or the selected venue becomes easier to manipulate.
A robust system therefore needs to consider not only how many sources exist, but also whether those sources provide meaningful and independent market coverage.
Crypto Oracle Manipulation and Bad Collateral Pricing
Collateral valuation is one of the most important areas of oracle risk.
Consider a lending market that accepts Token X as collateral.
If Token X is actually worth $1 but the oracle reports $10, a borrower could potentially deposit a comparatively small amount of Token X and borrow substantially more valuable assets.
When the oracle returns to the correct price, the protocol could be left with under-collateralized debt.
The reverse situation can also create unnecessary liquidations.
This is why protocols often use conservative loan-to-value ratios, liquidity checks, price caps, circuit breakers, and other safeguards in addition to an oracle.
Crypto Oracle Manipulation in 2026: Recent Exploits
Recent 2026 incidents demonstrate that oracle-related risk remains relevant.
In January, Makina lost approximately $4.13 million after a price-feed manipulation involving a Curve pool with significantly less liquidity than the temporary capital used during the attack.The Makina incident report provides the reported transaction details.
In February, YieldBlox suffered a roughly $10.97 million loss after an attacker manipulated an extremely thinly traded USTRY/USDC market. The exploit involved a price source that accepted the manipulated market price as collateral valuation.The YieldBlox incident analysis describes the attack mechanics.
In July, Bonzo Lend lost approximately $9.05 million on Hedera after an attacker exploited a verification flaw in a third-party Supra oracle contract.CoinDesk’s Bonzo Lend report details the incident.
Another July 2026 attack affected Ostium, where a manipulated reporting mechanism was used to trigger an approximately $18 million payout.CoinDesk’s Ostium coverage describes the use of falsified, future-dated oracle data.
These incidents do not mean every oracle system is unsafe. They illustrate that oracle design and integration remain important components of DeFi security.
Crypto Oracle Manipulation and 2026 DeFi Scale
The amount of capital secured by DeFi applications makes reliable price information particularly important.
The current DeFiLlama Ethereum snapshot reports approximately $54.34 billion in Ethereum DeFi TVL, while Ethereum-based DeFi shows roughly $536.9 million in 24-hour DEX volume in the same current snapshot.DeFiLlama’s Ethereum dashboard provides the live figures.
DeFiLlama’s Ethereum oracle dashboard currently lists 21 oracle categories or providers and shows Chainlink with approximately $12.02 billion in total value secured, Chronicle at about $5.09 billion, internal oracle systems at roughly $3.89 billion, and RedStone at around $2.33 billion.DeFiLlama’s Ethereum oracle dashboard provides the current methodology and provider-level figures.
These numbers are snapshots rather than fixed annual totals, but they show the scale at which oracle infrastructure is being used across DeFi.
How Protocols Reduce Crypto Oracle Manipulation Risk
Protocols can use several defensive techniques.
Multiple Data Sources
Combining data from multiple independent sources can reduce reliance on one market.
Time-Weighted Prices
TWAP mechanisms can make instantaneous manipulation more difficult.
Liquidity-Weighted Data
Prices can be derived from sufficiently deep markets rather than thin pools.
Outlier Filters
Extreme observations can be rejected when they fall outside defined parameters.
Heartbeat and Deviation Rules
Feeds can update when prices move significantly or when a defined time period passes.
Circuit Breakers
Protocols can temporarily restrict borrowing, withdrawals, or liquidations when an oracle becomes abnormal.
Conservative Collateral Parameters
Lower loan-to-value ratios can reduce the amount of damage from pricing errors.
Chainlink’s newerState Pricing approach illustrates another mitigation strategy: using end-of-block DEX state, weighted liquidity sources, and outlier filtering to reduce exposure to short-term price manipulation and flash-loan attacks.
How Developers Should Evaluate an Oracle
Before integrating an oracle, developers should investigate:
Data sources
Market coverage
Liquidity depth
Update frequency
Heartbeat
Deviation threshold
Node diversity
Data aggregation
Fallback behavior
Stale-price handling
Failure conditions
Historical performance
Emergency controls
A reputable oracle provider can still be integrated incorrectly.
The protocol must ensure that the feed’s assumptions match the asset and application.
For example, a price feed designed for a highly liquid asset should not automatically be assumed suitable for an obscure token trading primarily on one thin DEX pool.
Common Mistakes When Evaluating Crypto Oracles
Assuming a Decentralized Oracle Cannot Be Manipulated
Decentralization can reduce certain risks, but the quality of source data and the aggregation model still matter.
Looking Only at the Oracle Provider
The consumer protocol may introduce vulnerabilities through its own pricing logic.
Ignoring Market Liquidity
A thin underlying market can make even a well-designed price feed harder to secure.
Using Spot Prices Without Safeguards
Instantaneous DEX prices can be especially sensitive to large trades.
Ignoring Stale Data
A correct price from several minutes ago may still be inappropriate for a fast-moving market.
Treating Audits as Guarantees
An audit can reduce certain software risks but does not eliminate future oracle, market, governance, or operational failures.
Crypto Oracle Manipulation: Practical Checklist
Before trusting a DeFi price feed, check:
Source: Where does the price originate?
Coverage: How many markets contribute?
Liquidity: How deep are those markets?
Aggregation: How is the final price calculated?
Updates: How frequently does the feed update?
Heartbeat: How long can the value remain unchanged?
Deviation: What price movement triggers an update?
Outliers: Are abnormal observations filtered?
Fallback: What happens if the oracle fails?
Staleness: Can the protocol detect an old price?
Collateral: Are risk parameters conservative?
Circuit breaker: Can extreme conditions pause sensitive actions?
History: Has the feed or integration experienced prior incidents?
Crypto Oracle Manipulation is an important DeFi security risk because many blockchain applications depend on external or market-derived prices to calculate collateral, liquidations, trading values, and settlement conditions.
An attack does not necessarily require compromising the oracle provider itself. An attacker may instead manipulate a thin liquidity pool, exploit a weak aggregation method, submit incorrect data through a flawed verification mechanism, or take advantage of stale pricing.
The 2026 Makina, YieldBlox, Bonzo Lend, and Ostium incidents demonstrate several different versions of this risk.
At the same time, Ethereum DeFi continues to secure tens of billions of dollars, making robust price infrastructure increasingly important.
The strongest approach is to evaluate data sources, liquidity, aggregation, update frequency, stale-price protection, outlier handling, fallback mechanisms, and protocol-level risk controls together.
The key question is not simply:
“Which oracle does the protocol use?”
It is:
“How does the protocol obtain, validate, and safely use the price before allowing money to move?”
FAQs
1. What is Crypto Oracle Manipulation?
Crypto Oracle Manipulation occurs when an attacker influences or exploits the price-data mechanism used by a blockchain application so that the application receives an inaccurate or misleading value.
2. Why do DeFi protocols need price oracles?
Smart contracts cannot directly access external market information. Oracles provide data such as cryptocurrency prices that lending, derivatives, stablecoin, and synthetic-asset protocols need.
3. How can an attacker manipulate an oracle?
An attacker may manipulate a thin market, exploit weak data aggregation, influence a faulty data source, exploit an oracle contract, or take advantage of stale or improperly validated prices.
4. What role do flash loans play in oracle attacks?
Flash loans can provide large temporary amounts of capital that can be used within a single transaction to manipulate low-liquidity markets.
The January 2026 Makina exploit demonstrated this attack pattern.
5. What happened in the Makina oracle exploit?
Attackers used a 280 million USDC flash loan and manipulated Makina’s pricing mechanism before trading against a pool with roughly $5 million in liquidity. Reported losses were approximately $4.13 million.
6. Can a decentralized oracle still have risks?
Yes.
A decentralized network can reduce reliance on one source, but risks can remain in data quality, market coverage, aggregation logic, update frequency, integration code, and underlying liquidity.
7. What is a TWAP oracle?
A TWAP, or Time-Weighted Average Price, calculates an average price over a defined period rather than relying entirely on one instantaneous market price.
8. What is a stale oracle price?
A stale price is a value that has not been updated sufficiently to reflect current market conditions.
Stale prices can become particularly problematic during rapid market movements.
9. What is an oracle circuit breaker?
A circuit breaker is a protocol-level safety mechanism that can temporarily restrict sensitive operations when an oracle price becomes abnormal or unreliable.
10. Are oracle attacks always caused by the oracle provider?
No.
A vulnerability can exist in the way a DeFi protocol consumes the oracle, the market from which the price is derived, or the logic connecting the price to collateral and trading decisions.
11. How can users identify oracle risk in a DeFi protocol?
Look for documentation describing the oracle source, data aggregation method, market coverage, update frequency, stale-price protection, fallback behavior, and collateral-risk parameters.
12. Where can I learn more about Crypto Oracle Manipulation?
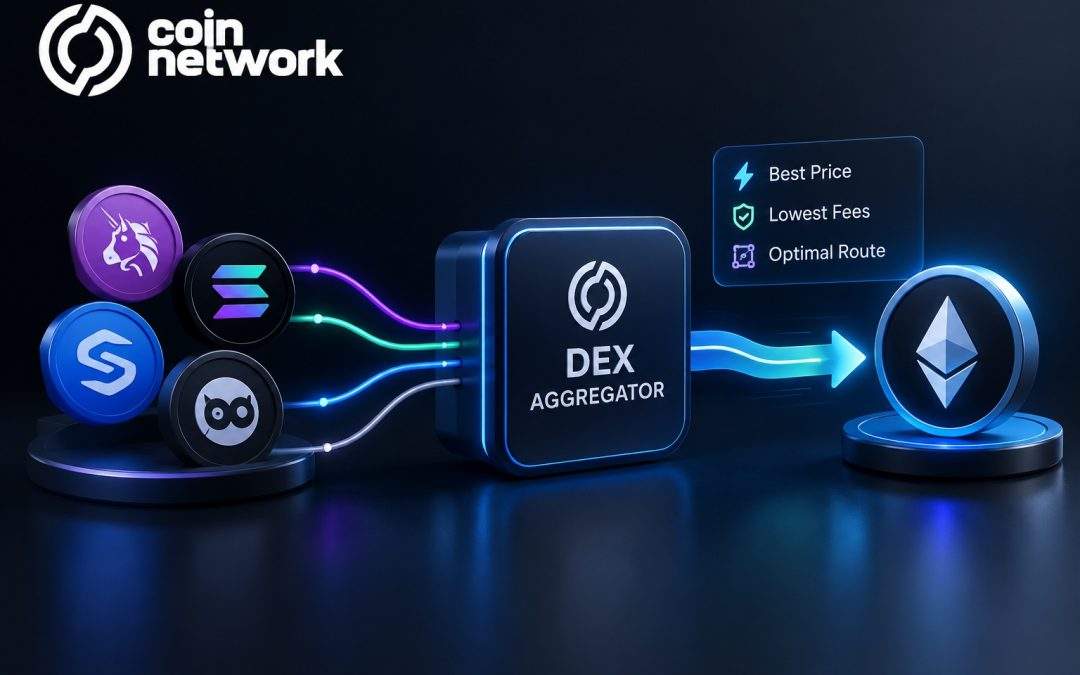
DEX Aggregators are crypto trading services that search across multiple decentralized exchanges and liquidity sources to determine a potentially better route for a token swap.
Instead of asking a trader to compare Uniswap, Curve, SushiSwap, Balancer, and other liquidity venues manually, an aggregator can evaluate available routes and present a single trade option.
Ethereum.org describes 1inch as an exchange aggregator that scans decentralized exchanges to find competitive prices, while its DeFi overview also lists aggregators such as CoW Swap that combine liquidity and routing strategies.Ethereum’s DeFi ecosystem overview provides broader context.
The main idea is simple:
More liquidity sources can give a routing system more options to compare.
However, the route with the highest quoted output is not always the route with the lowest total economic cost. Gas, price impact, fees, slippage, execution risk, and MEV can all matter.
How DEX Aggregators Work
A typical DEX aggregator performs several steps after a user enters a trade.
Suppose a trader wants to swap 10 ETH for USDC.
The aggregator can examine liquidity from multiple markets and estimate how much USDC each route could produce.
It might find:
Direct ETH → USDC on one DEX
ETH → USDT → USDC through two pools
ETH → WETH → USDC through another route
A split trade using several DEXs
A route combining AMM liquidity with professional market-maker liquidity
The routing engine then compares the expected outcome.
The user usually sees one quote even though the transaction may involve multiple liquidity sources.
The exact routing methods differ by provider, but the objective is generally to optimize execution rather than simply choose the exchange with the highest displayed token price.
DEX Aggregators and Liquidity Fragmentation
DEX liquidity is fragmented across many protocols and chains.
A token pair may have liquidity on multiple automated market makers, concentrated-liquidity pools, order-based systems, and professional market-maker networks.
This fragmentation creates both a challenge and an opportunity.
A trader using one DEX may see only the liquidity available on that platform.
An aggregator can compare several venues.
For example,1inch explains its aggregation model as a system that searches multiple DEXs and can split a trade among different liquidity sources.
The benefit can become more noticeable for larger trades because the trader is less dependent on a single pool.
DEX Aggregators and Smart Order Routing
Smart order routing is the main technology behind modern DEX aggregation.
The router can evaluate multiple paths instead of simply selecting the cheapest-looking pool.
Imagine these simplified options:
Route A: ETH → USDC = $30,000
Route B: ETH → USDT → USDC = $30,040
Route C: 60% through DEX A + 40% through DEX B = $30,090
A smart router may choose Route C because the combined result is better under the current liquidity conditions.
The calculation can include:
Expected output
Pool depth
Price impact
Trading fees
Gas costs
Route complexity
Available liquidity
Quote freshness
This is why the term “best route” should generally mean the best estimated execution result, not simply the highest quoted spot price.
DEX Aggregators and Split Trades
One important feature is the ability to split a transaction.
A large swap can move the price in one pool if that pool does not have enough liquidity.
Instead of sending the full transaction through one source, an aggregator can divide the order.
For example:
40% through DEX A
35% through DEX B
25% through DEX C
This can reduce the price impact associated with using one pool.
1inch’s routing documentation specifically describes transaction splitting as a way to spread larger trades across multiple liquidity sources.
However, splitting does not always improve the final result. Additional contract calls can increase gas consumption, and the optimal route depends on the size and structure of the trade.
DEX Aggregators and Multi-Hop Routes
Sometimes the best route is not a direct swap.
A token pair may have limited direct liquidity but deep liquidity through an intermediate asset.
For example:
TOKEN A → USDC → TOKEN B
or:
TOKEN A → WETH → TOKEN B
This is known as a multi-hop route.
Intermediate tokens can act as bridges between fragmented liquidity pools.
Uniswap’s technical walkthrough explains how swap paths can contain multiple exchanges, with routers moving through the specified sequence of pairs.
Aggregators can evaluate these paths alongside direct routes.
The trade-off is that more hops can mean more contract interactions, more gas, and potentially more execution complexity.
DEX Aggregators and Gas Costs
A route with the best token output is not necessarily the cheapest trade.
Suppose:
Route A returns $10,000 and costs $5 in gas.
Route B returns $10,015 but costs $25 in gas.
The second route has a higher gross output but may produce a worse net result after transaction costs.
Gas therefore needs to be included in route optimization.
This becomes especially important on Ethereum when network demand increases.
Ethereum’sDEX design guidance recommends displaying important trade information such as price impact, slippage, expected output, minimum received, gas cost, and other fees.
For traders, this means a good aggregator quote should be evaluated using net execution value, not just the headline output number.
DEX Aggregators, Slippage, and Price Impact
Slippage and price impact are related but different.
Price impact describes the effect that the trade itself has on the market price because of available liquidity.
Slippage is the difference between the expected execution and the amount ultimately received, including movements between quoting and execution.
An aggregator can reduce price impact by finding deeper liquidity or splitting a trade, but it cannot eliminate market movement.
A quote is also not guaranteed forever.
A fast-moving market can change before the transaction reaches the chain.
That is why users should review:
Expected output
Minimum received
Price impact
Slippage tolerance
Gas estimate
Quote expiry
DEX Aggregators and RFQ Liquidity
Modern aggregators do not always rely exclusively on public AMM pools.
Some also use RFQ, or Request for Quote, liquidity from professional market makers.
0x’s June 2026 documentation says its Swap API aggregates liquidity across 150+ DEXs and supports 20+ EVM-compatible chains. It also describes routing across AMMs and professional market makers.0x’s 2026 API overview provides the current details.
Its RFQ documentation states that for selected major trading pairs, RFQ liquidity produced a better price than AMMs around 52% of the time in its measured sample. The document also explains that 0x can combine RFQ and AMM liquidity in a single route.0x’s RFQ explanation provides the methodology and limitations behind that figure.
This is an important development because aggregation increasingly means comparing different types of liquidity, not merely different DEX pools.
DEX Aggregators and MEV
Maximum extractable value, or MEV, can affect swap execution.
A pending transaction can potentially be observed and reordered by market participants depending on the blockchain and transaction flow.
Some trading systems attempt to reduce exposure through private order flow, batch auctions, intent-based execution, or professional market-maker systems.
For example, Ethereum.org describes CoW Swap as a DEX aggregator that uses frequent batch auctions and peer-to-peer matching to seek liquidity while reducing certain forms of MEV exposure.Ethereum’s CoW Swap overview provides more context.
This means traders should not assume every aggregator uses the same execution model.
DEX Aggregators in 2026
DEX aggregation is now a substantial part of decentralized trading infrastructure.
A current DeFiLlama snapshot for Ethereum shows approximately $258.66 million in DEX-aggregator volume over 24 hours and $16.97 billion over 30 days. The same dashboard lists 1inch at roughly $2.13 billion in 30-day aggregator volume, 0x at about $2.58 billion, and CoW Swap at around $3.15 billion.DeFiLlama’s Ethereum DEX Aggregator dashboard provides the continuously updated figures.
For comparison, DeFiLlama’s Ethereum DEX dashboard currently shows approximately $557.46 million in 24-hour DEX volume and $39.51 billion over 30 days.The Ethereum DEX volume dashboard provides the corresponding ecosystem-wide snapshot.
These figures should be treated as live market data rather than fixed 2026 annual totals. Aggregator volume can also involve overlapping liquidity sources and different reporting methodologies, so simple comparisons between individual dashboards should be made carefully.
DEX Aggregators: What Makes a Route “Best”?
The best route depends on what the trader is optimizing.
A route can be evaluated based on:
Highest Expected Output
Useful when price is the primary concern.
Lowest Total Cost
Combines output, gas, and applicable fees.
Lowest Price Impact
Important for larger or less liquid trades.
Lowest Execution Risk
A simpler route may have fewer moving parts.
MEV Protection
Relevant when transaction ordering could materially affect execution.
Fast Execution
Some systems prioritize execution reliability over a small theoretical improvement in output.
The best aggregator therefore is not necessarily the one that always displays the highest quote. It is the one whose execution model best matches the user’s priorities and the current market.
Limitations of DEX Aggregators
Aggregation does not eliminate trading risks.
An aggregator can still route through:
Low-liquidity pools
Vulnerable protocols
Token contracts with transfer restrictions
Tokens with unusual taxes
Reverting liquidity sources
Complex multi-hop paths
A routing engine also depends on accurate quotes and available liquidity.
Users should inspect the final transaction before signing and verify that the received amount, token address, slippage limit, and contract interaction match their intentions.
For broader crypto-security education, Coin Network’sCryptopedia can be useful alongside itsDeFi coverage.
How to Use DEX Aggregators Safely
Before confirming a swap:
Check the Token
Verify the contract address rather than relying only on the ticker.
Compare the Quote
Look at expected output, price impact, and total fees.
Review the Route
Understand whether the trade is direct, split, or multi-hop.
Check Slippage
A very high slippage tolerance can expose a trade to worse execution.
Review Gas
A complex route may require more gas.
Check Approvals
Confirm which token and spender the approval transaction targets.
Review the Final Transaction
Make sure the destination contracts and output assets match the intended trade.
Coin Network’scrypto wallet security guide provides additional guidance on approvals, suspicious dApps, and transaction review.
Common Mistakes When Using DEX Aggregators
Assuming the Aggregator Guarantees the Best Price
Quotes change rapidly and depend on the available liquidity and gas conditions.
Ignoring Gas Costs
A slightly better gross output can become worse after execution costs.
Using Excessive Slippage
A generous slippage setting may make a trade more tolerant but can also increase execution risk.
Ignoring Price Impact
A route can still produce significant market impact when liquidity is thin.
Assuming Every Route Is Equally Safe
Different routes can interact with different contracts and liquidity sources.
Comparing Only the Headline Token Output
Always consider fees, gas, price impact, and minimum received.
DEX Aggregators: Practical Checklist
Before confirming a crypto swap, check:
Quote: What is the expected output?
Route: Which DEXs or liquidity sources are being used?
Split: Is the trade divided among multiple pools?
Price impact: How much does the order move the market?
Slippage: What is the maximum acceptable execution difference?
Gas: How much will the transaction cost?
Fees: Are there aggregator or protocol fees?
Token: Is the contract address correct?
Approval: Which spender receives token permission?
MEV: Is the execution model exposed to ordering risk?
Minimum received: What is the minimum output after tolerance?
Transaction: Does the final wallet request match the quote?
Conclusion
DEX Aggregators make decentralized trading more efficient by comparing fragmented liquidity and automatically selecting or constructing routes for token swaps.
Instead of relying on a single DEX, traders can access direct routes, multi-hop paths, split trades, and in some cases professional RFQ liquidity.
The current 2026 market data shows that aggregation is already a substantial part of Ethereum’s trading infrastructure, with DeFiLlama currently recording about $258.66 million in 24-hour Ethereum DEX-aggregator volume and approximately $16.97 billion over 30 days.
However, aggregation is not the same as a guarantee of perfect execution.
Gas, price impact, slippage, MEV, liquidity quality, token behavior, and smart-contract risk can all affect the final result.
The most useful approach is to treat a DEX aggregator as a routing and execution tool, then review the proposed transaction before signing.
The key question is:
Does the selected route provide the best overall execution after liquidity, price impact, gas, fees, and execution risk are considered?
FAQs
1. What are DEX Aggregators?
DEX Aggregators are platforms or protocols that compare liquidity across multiple decentralized exchanges and attempt to find an efficient route for a token swap.
2. How do DEX Aggregators find the best route?
They compare available liquidity, prices, fees, gas requirements, and potential paths across different sources.
Some systems can split a trade or use multiple hops when that produces a better estimated result.
3. Are DEX Aggregators better than using one DEX?
They can provide more routing options because they can compare multiple liquidity sources.
However, the best choice depends on the trade, chain, liquidity conditions, gas costs, and execution model.
4. Can DEX Aggregators split a trade?
Yes.
A routing system can divide a single order among multiple liquidity sources when doing so is expected to improve execution.
5. What is smart order routing?
Smart order routing is the process of evaluating multiple possible execution paths and selecting a route based on factors such as output, liquidity, price impact, gas, and fees.
6. What is a multi-hop swap?
A multi-hop swap passes through one or more intermediate assets.
For example, a trade might use Token A → USDC → Token B instead of exchanging Token A directly for Token B.
7. Do DEX Aggregators reduce slippage?
They can reduce price impact by finding deeper liquidity or splitting trades, but they cannot eliminate market movement or guarantee a specific execution price.
8. Do DEX Aggregators charge extra fees?
Some aggregators may charge a routing or service fee, while others monetize through other mechanisms.
Traders should review the quote’s fee information before signing.
9. What is RFQ liquidity in a DEX Aggregator?
RFQ, or Request for Quote, allows professional market makers to provide trade-specific quotes.
Some aggregators compare those quotes with public AMM liquidity and use whichever route offers the stronger execution result.
10. Can DEX Aggregators protect against MEV?
Some execution systems are designed to reduce particular MEV risks, but protection varies by aggregator and transaction method.